Europe prepares for a regulatory rearmament of the digital: the new frontier of power is in the algorithms

Brussels prepares for the return a regulatory rearmament on the digital agenda, cybersecurity, and telecommunications while the Twenty-Seven elevate technological sovereignty to the highest political level.

ILUSTRACIONES (1200 x 675 px) (1200 x 675 px)

ILUSTRACIONES (1200 x 675 px) (1200 x 675 px)

Add DEMÓCRATA to Google

Ask FREN

Published

Last updated

8 minutes

Most read

Elecciones 29N · Encuestas

La media de las encuestas

Media a 21 de octubre de 2026 · 15 institutos

  • PP31,6 %
  • PSOE26,9 %
  • Vox18,7 %
  • Sumar6,3 %
  • Podemos3,1 %
  • ERC2,2 %
010203040ene 2024jul 2024ene 2025jul 2025ene 2026jul 2026

Media del último estudio de cada instituto en 30 días y su evolución semanal desde el 23J. Partidos con al menos un 2 %.

Todas las encuestas

Elecciones generales del 29 de noviembre · Demócrata

The digital wallet has monopolized a good part of the conversations in Brussels over the last few months, but no one considers the discussions closed in view of the new political course. Community legislators are preparing for a new technological offensive in a long-range battle with which the European Union aims to strengthen its digital sovereignty and reduce its strategic dependencies.

New regulatory frameworks for Artificial Intelligence, cybersecurity, and telecommunications will again take center stage in much of the community debates after the holiday break. The objective is no longer solely to regulate the risks associated with new technologies, but to determine who controls the infrastructures, the providers, and the industrial capacities that will sustain the European economy in the coming decades.

According to what Demócrata has been able to confirm, digital matters have acquired such magnitude that the president of the European Council would have conveyed to the heads of State and Government of the Twenty-Seven his intention to, for the first time, include a specific item on the agenda of an upcoming European Council summit in Brussels dedicated to advances in disruptive new technologies.
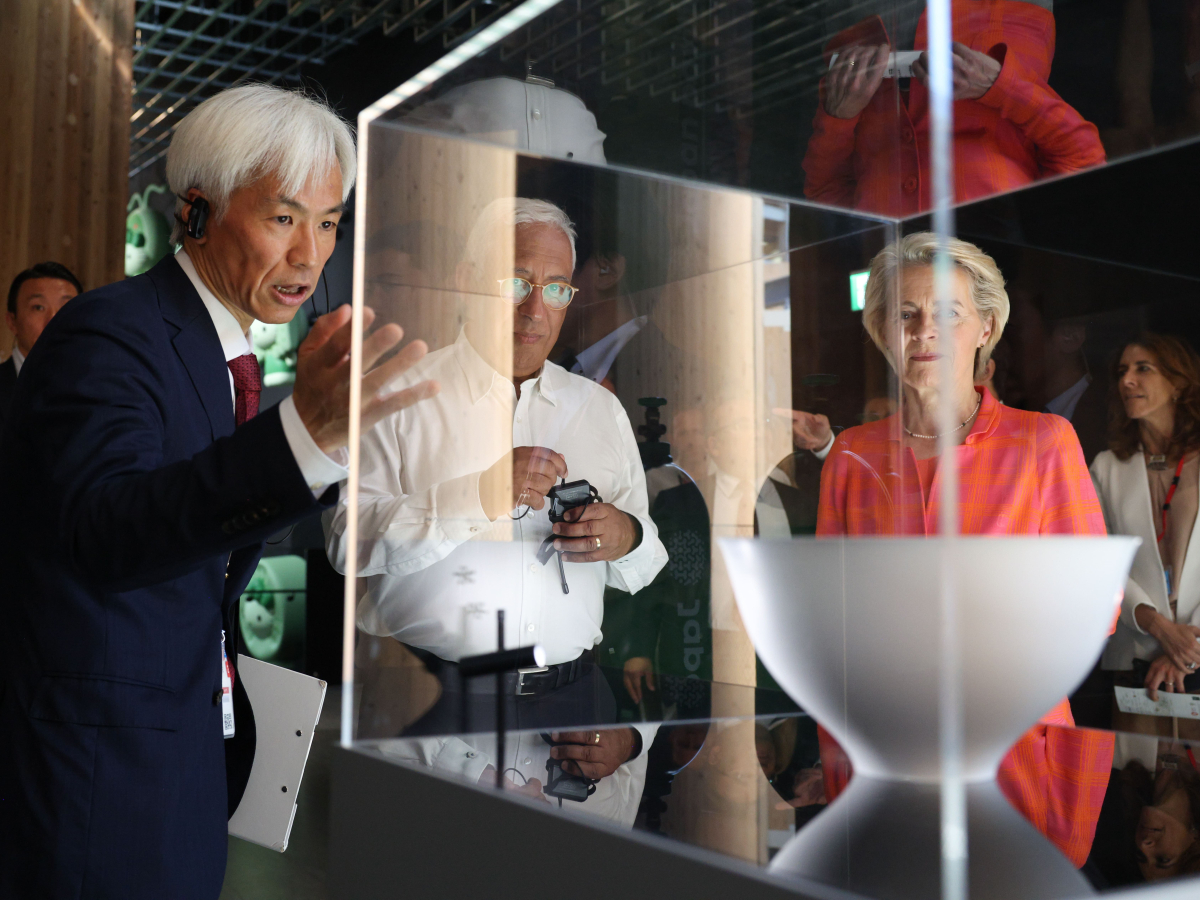
European Council
European Council -

Digital transformation has thus become one of the major legislative priorities of the second term of the president of the European Commission, Ursula von der Leyen, and Brussels is willing to elevate its processing and political discussion to the highest institutional level.

In a letter addressed to the heads of Government of the Twenty-Seven in February, the president of the community Executive acknowledged that "digital and Artificial Intelligence will profoundly transform all aspects of our economies". A statement that summarizes the shift in focus that European technology policy has experienced: from sectoral regulation to a cross-cutting strategy directly linked to competitiveness, economic security, and strategic autonomy.

From regulatory leadership to "technological rearmament"

The truth is that, little by little, the European Commission has been showing its cards in what can already be defined as a «European technological rearmament». After an initial period in which the continent was a world pioneer in regulating areas such as Artificial Intelligence, Brussels has begun to review how to apply that regulatory framework without compromising the ability of European companies to compete.

Last November, the Commission adopted what is known as "Digital Omnibus", with the intention of simplifying or adjusting certain elements of the European Artificial Intelligence framework. The review came at a particularly sensitive moment, with the implementation of new regulatory obligations and the growing pressures from the industry to prevent bureaucratic burdens from becoming a competitive disadvantage.

In practice, the process involved extending certain flexibilities and adaptation mechanisms, especially for small and medium-sized enterprises, while opening an intense debate about the limits of regulatory simplification.

If the co-legislators were able to come away with something to celebrate from those negotiations, it was the introduction of the prohibition of certain "deepfake" tools and systems known as "nudification" through Artificial Intelligence. The measure responds to the attempt to strengthen protection against the generation of non-consensual sexual content and child abuse material.

The battle in the negotiation room revolved precisely around avoiding excessive delays in the implementation of the new obligations. Ultimately, the timeline ended up consolidating an extension for certain elements over the next two years, without giving up on incorporating new prohibitions related to the most harmful uses of Artificial Intelligence.
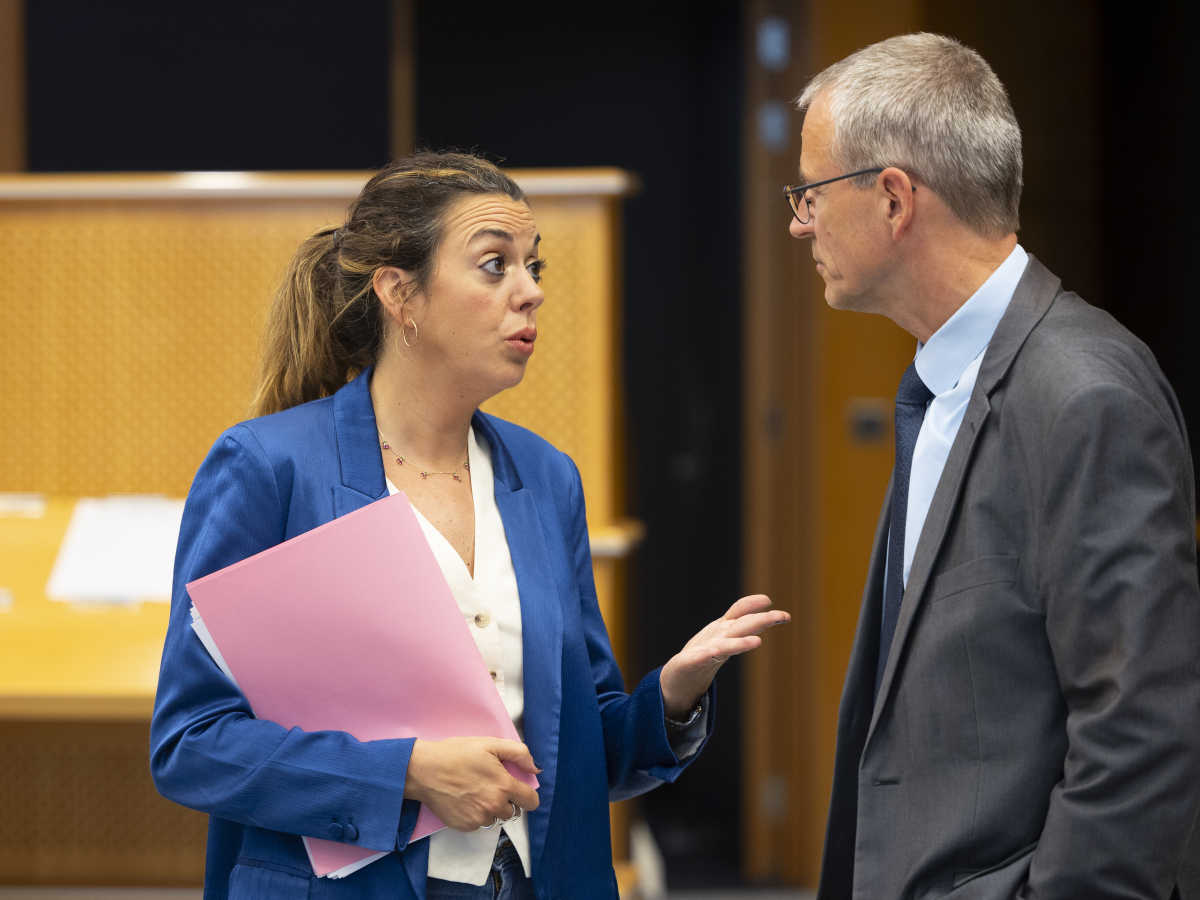
Laura Ballarín - European Parliament
Laura Ballarín - European Parliament -

"At the same time that the prohibition of these nudification systems through Artificial Intelligence was included, we managed to maintain the obligation of digital literacy," said Laura Ballarín, the MEP and negotiator for the Socialist Group, in a conversation with Demócrata.

The position of the Eurochamber, as the socialist explained, was to defend that "this omnibus could not serve to roll back" the guarantees already achieved during the negotiation of the European legislation on Artificial Intelligence.

The new "cookies"

At the same time, Brussels reinforced its strategy with the presentation of a plan to create a European single window aimed at simplifying compliance with cybersecurity incident notification obligations.

The approach aims to reduce the regulatory fragmentation that many companies currently face, forced in certain cases to report the same incident to different national and European authorities depending on the applicable legislation.

The proposed simplification also ended up extending to the consent system for "cookies", one of the main symbols of everyday digital bureaucracy for citizens and businesses. The goal is to reduce the number of notices that appear during browsing and allow users to indicate certain preferences through a more centralized system.

The model would allow, among other issues, to save consent settings through browsers and reduce the repetition of requests, although the legal debate on data protection and the effective scope of consent remains open.

Cybersecurity, the core of strategic autonomy

The other major axis of the community digital offensive has focused on cybersecurity. During the last political term, the European Executive presented various initiatives aimed at deploying a new legal and operational framework to respond to the increasing sophistication of digital threats.

Through the EU Action Plan on Cybersecurity and Artificial Intelligence, Brussels seeks to define mechanisms to assess and mitigate the risks associated with advanced AI models, while strengthening the capabilities of the European Union Agency for Cybersecurity, ENISA. The Commission foresees, in this line, the development of a European platform for testing Artificial Intelligence applied to cybersecurity, with the aim of analyzing both the defensive potential of these technologies and the new attack vectors they may generate.

One of the most sensitive points of the reforms lies in the future European Cybersecurity Law, especially regarding the management and protection of telecommunications networks.
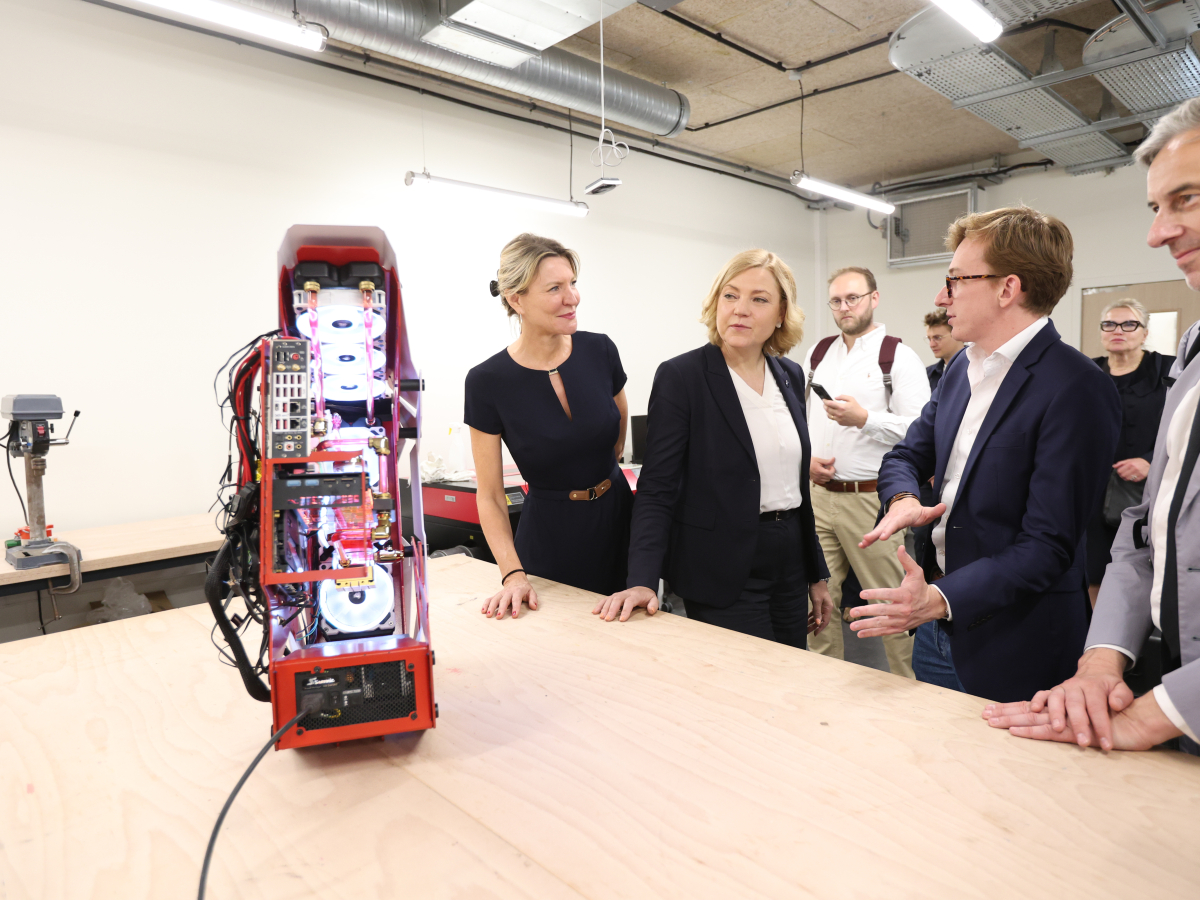
Sophie Viger, coding school 42's Director, left, and Henna Virkkunen, center, durign a visit to coding school 42, in Paris, France.
Sophie Viger, coding school 42's Director, left, and Henna Virkkunen, center, durign a visit to coding school 42, in Paris, France. -

The Commission has promoted a mandatory reduction of risks in mobile networks, particularly regarding those providers considered to be “high risk”. A matter that directly affects companies like Huawei and has generated friction between Brussels and some member states.

This issue has a direct impact in Spain, where the Government maintains active contracts with Chinese companies. During the last quarter of the past political term, the community Executive issued a warning to Spain regarding the dependencies that could arise from a concession linked to the storage of telephone interceptions from the SITEL system.

The community Executive has already identified on several occasions the Chinese operators Huawei and ZTE as suppliers that present “significantly greater risks” compared to other players in the 5G network market. Consequently, Brussels has committed to limiting their access to certain avenues of European funding and to strengthening the protection of corporate and institutional communication networks on the continent.

In light of this legislative file, sources from Moncloa consulted by Demócrata defended that it should be the member States themselves who maintain decision-making capacity on whether a country, a supplier, or a product poses excessive structural risks.

A position that also extends to decisions on which assets and information and communication technologies should be considered essential from a security standpoint.

“We argue that this classification should be based on objective, proportionate, and viable technical criteria that guarantee legal security for all parties and respect national sovereignty,” they stated during the negotiations from the Ministry for Digital Transformation and Public Function, led by Óscar López.

The major telecommunications reform

At the same time, at the beginning of this year, the cabinet of the executive vice president Henna Virkkunen announced its proposal for a Digital Networks Regulation, intended to replace, once it comes into force, the current European Electronic Communications Code.

The initiative aims to update the regulatory framework for telecommunications to adapt it to a scenario marked by the deployment of very high-capacity networks, the expansion of data centers, the development of cloud computing, and the increasing dependence on critical digital infrastructures.
"The European innovation begins with a truly connected Europe. A resilient and high-performance digital infrastructure is essential to reinforce Europe's leadership in innovation, competitiveness, and digital sovereignty", noted Virkkunen during the presentation of the proposal in Strasbourg.

The message summarizes the philosophy of the new community stage: connectivity has ceased to be considered solely an economic service to become a strategic infrastructure.

Chips, cloud, open source, and quantum computing

The last link in this chain before the political rentrée was the presentation of the Technology Sovereignty Package, aimed at strengthening the industrial capacity of the continent and consolidating a European digital infrastructure capable of competing with the United States and China.

The strategy is articulated around several pillars:

  • Chips Regulation: aimed at reinforcing production, supply, and European resilience in the field of semiconductors.

  • Cloud Development Law: aimed at significantly increasing European data center capacity and promoting infrastructure and storage solutions considered strategic.

  • Open Source Strategy: designed to reinforce European autonomy in software, digital tools, and reusable technologies.

  • European Quantum Law: conceived to boost research, industrial development, and the deployment of European capabilities in computing and quantum technologies.

The new community bet implies, in practice, a paradigm shift in the digital policy of the European Union.

Brussels seeks to abandon a merely reactive position, fundamentally focused on resilience and response to external risks, to adopt a more assertive strategy aimed at controlling the critical technologies that will determine the economic, industrial, and political balance of the coming decades.
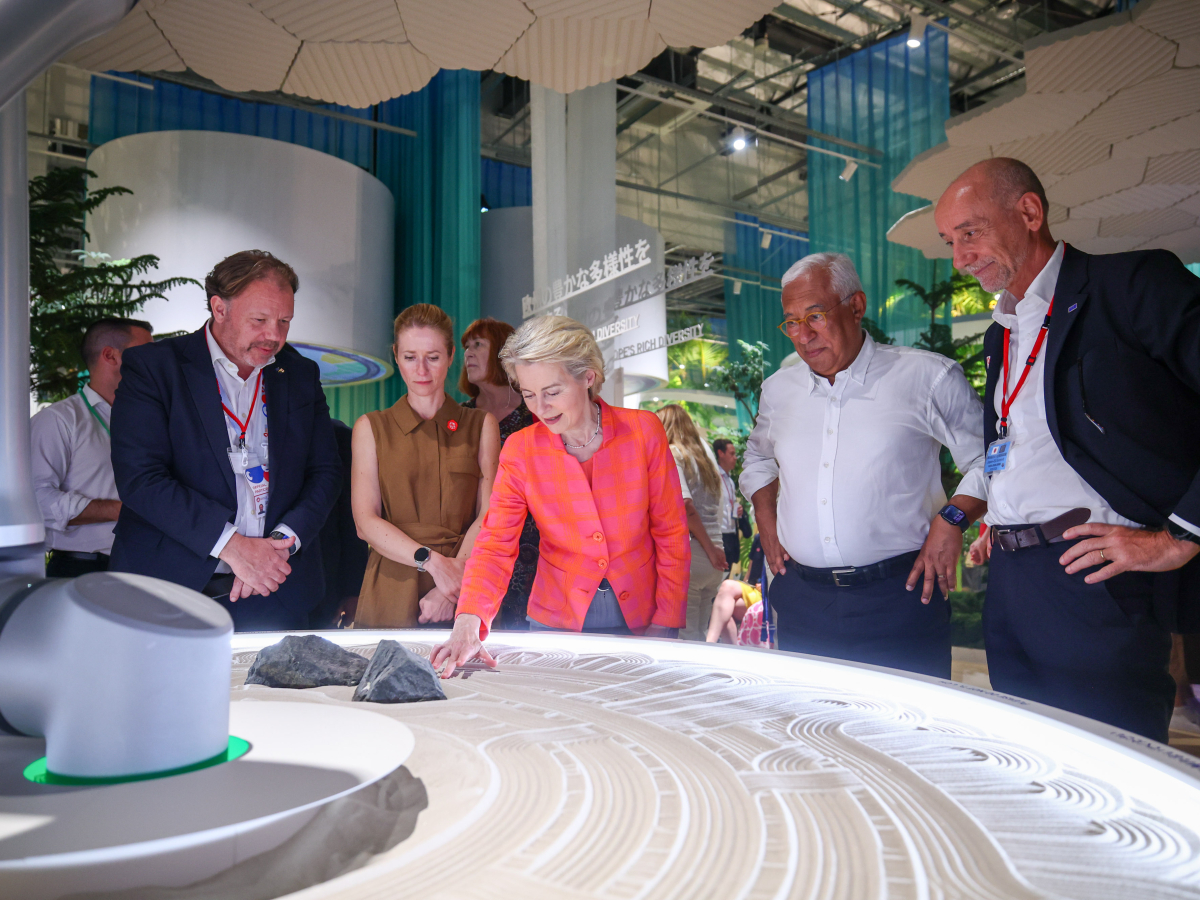
Kaja Kallas, Ursula von der Leyen, and António Costa, from left to right
Kaja Kallas, Ursula von der Leyen, and António Costa, from left to right -

The ultimate aspiration is that the European Union can continue to be a global partner open to trade and international cooperation, but that, at the same time, has the necessary technological tools to act autonomously when its strategic interests require it.

In a context marked by technological rivalry between the United States and China, the European Commission seems to have definitively assumed that digital sovereignty has ceased to be an exclusively industrial or regulatory issue.

The control of networks, data, semiconductors, Artificial Intelligence, the cloud, and quantum technologies has become a central element of the economic and geopolitical security of the European project. And, after the holiday break, Brussels is preparing to take that battle to a new political dimension.

More key points, information and questions with FREN

AI-GENERATED CONTENT

What parliamentary phase is the European Cybersecurity Act currently in, and what are the next steps for its final approval?

Based on the available information, the so-called “European Cybersecurity Act” you refer to is the new Cybersecurity Regulation proposal presented by the Commission on January 20, 2026, which reviews and strengthens the framework of the current Cybersecurity Act and its European certification system. This proposal has not yet been definitively approved: it is currently in the ordinary legislative procedure (European Parliament and Council) and without a finalized text.

1. Exact phase

According to the legislative analysis by Demócrata, the Commission presented the new EU Cybersecurity Regulation as part of a cybersecurity package aiming to:

  • Strengthen the EU's capacity to prevent, detect, and respond to large-scale cybersecurity incidents.
  • Update the European Cybersecurity Certification Framework, simplifying and harmonizing schemes.
  • Reduce regulatory fragmentation and ICT supply chain risks, including risks linked to third-country suppliers.

After this presentation, the text “now begins its ordinary legislative procedure”, which implies:

  • In the European Parliament, examination by the competent committees on the internal market, civil liberties, and security, which must prepare reports and amendments.
  • In the Council, Member States must establish a position on the scope of the new framework and its alignment with existing or transposed legislation (for example, NIS2).

Other recent articles indicate that the reform of the EU cybersecurity law and the new certification framework “are still in the legislative process” and that the final form of the regulation must still be negotiated with the Twenty-Seven and the European Parliament, confirming that, as of August 2026, final approval has not yet occurred.

2. Next steps in the European parliamentary procedure

From the current phase (Commission proposal under study), the usual steps until final approval are:

  • 1) Work in European Parliament committees
    The committees (e.g., Internal Market, Civil Liberties, and Security) discuss the text, present amendments, and approve a report with the Parliament's position. This report will serve as the basis for the Plenary debate.
  • 2) Formation of the Council's position
    In parallel, Council working groups and competent ministers agree on a general position, in which Member States adjust the scope of the regulation, certification obligations, ENISA governance, etc.
  • 3) Trilogues
    With the Parliament and Council positions on the table, interinstitutional negotiations (trilogues) open between:
    • European Commission (defending the initial proposal and mediating technically);
    • European Parliament (rapporteur MEPs and “shadows”);
    • Council (representatives of Member States).
    The goal is to reach a single compromise text.
  • 4) Formal approval
    Once the political agreement is closed, both the Parliament Plenary and the Council must formally approve the regulation. Only then is it sent to the Official Journal of the EU (OJEU) for publication.
  • 5) Entry into force and application
    The regulation normally enters into force 20 days after its publication, but many cybersecurity and certification obligations apply after transitional periods (e.g., 24 months), as has happened with the Cyber Resilience Act or the Cyber Solidarity Act.

3. What it implies for companies and Member States

Although the “European Cybersecurity Act” is not yet approved, the pieces of the new European framework are already being deployed:

  • ENISA has promoted schemes such as the EUCC (certification based on common criteria) and is working on others, including for managed security services, in accordance with the current Cybersecurity Act and future amendments.
  • The Commission and Council have already adopted other regulations in the package, such as the Cyber Solidarity Act, and are advancing in the implementation of NIS2, DORA, and the Cyber Resilience Act, which will be applied gradually between 2026 and 2028 (see analysis).
  • Member States, like Spain, are reorganizing their own national cybersecurity laws to align with this European package and the future cybersecurity regulation currently under negotiation.

In summary, the European Cybersecurity Act strictly speaking (the new regulation revision) is today in parliamentary and Council negotiation phase, without a final vote, and the next milestones will be the closure of positions by both institutions, the trilogues, and the formal adoption of the regulation, after which a gradual implementation period and development of new European certification schemes will begin.

What powers are attributed to the President of the European Commission, Ursula von der Leyen, regarding digital transformation according to EU treaties?

The powers of the President of the European Commission in digital transformation do not appear as a “specific catalog” in the EU Treaties. What exists is, on one hand, the general framework of the Commission's powers and, on the other, the functions that the Treaties attribute to the President of the Commission. From there, the digital dimension is framed as one of the major political priorities, but legally it is exercised through those general powers.

1. General basis: the role of the Commission in digital policies

Digital transformation is articulated in the Treaties mainly as part of the internal market, trans-European networks, research and innovation, and data protection, among other areas. Although the question focuses on the President, it is important to remember that:

  • Article 17.1 of the TFEU establishes that the Commission “shall promote the general interest of the Union and take appropriate initiatives to that end.”
  • Article 17.2 TFEU indicates that, with few exceptions, the Commission has the monopoly on legislative initiative (it presents proposals for regulations, directives, decisions, etc.).
  • Much of the digital legislation (digital services, digital markets, cybersecurity, data, 5G networks, etc.) is based on the articles of the TFEU on the internal market, trans-European networks, information society, or research.

That is, the Union's capacity to act digitally is legally channeled through the Commission as a whole, and the President exercises her powers within that collegiate framework.

2. Formal powers of the President according to the Treaties

The President's functions are mainly described in Article 17.6 TFEU and, more generally, in other provisions on the functioning of the Commission. The most relevant, with direct impact on the digital agenda, are:

  • Setting the general political direction of the Commission (art. 17.6 TFEU): the President “shall lay down the guidelines on which the Commission shall be based in carrying out its tasks.” This includes deciding that digital transformation is a strategic priority and defining its main lines (for example, a “Europe prepared for the digital age”).
  • Organizing the Commission internally: the same article grants her the power to “decide the internal organization of the Commission to ensure coherence, efficiency, and collegiality of its action.” On this basis, the President:
    • Assigns and can reassign portfolios (for example, an executive vice-president responsible for the digital agenda).
    • Determines which commissioner leads specific digital legislative proposals.
    • Restructures services (directorates-general) to adapt them to the digital priority.
  • Appointing and, if necessary, dismissing commissioners within the provided margins: the President “shall decide the distribution of responsibilities among the members of the Commission” and can request a commissioner’s resignation. This gives her decisive political leverage over who drives the digital agenda.
  • Leading the work of the College: she chairs the meetings of the College of Commissioners, sets the agenda, and therefore can prioritize or delay legislative and strategic proposals on digital matters.
  • Representation of the Commission: the President represents the Commission before the European Council, the Council, and the European Parliament (without prejudice to the High Representative in the CFSP). This includes:
    • Defending the Commission's digital initiatives in legislative negotiations.
    • Participating in European councils where digitalization (data, artificial intelligence, cybersecurity) is a central topic.

3. Specifics regarding digital transformation

Based on these general provisions, Ursula von der Leyen's powers regarding digital matters are concretized in several types of acts and decisions:

  • Establishing the initial “political guidelines” for the legislature, in which she can identify digital transformation as a cross-cutting priority (data economy, AI, connectivity, digital capabilities, etc.).
  • Proposing and coordinating the Commission's annual work program, which includes the digital legislative and non-legislative initiatives the Commission plans to present.
  • Promoting the use of the right of initiative in digital matters: although proposals are prepared by the competent commissioner, the President can order, prioritize, or redirect those proposals (for example, accelerating an AI regulation or modulating its scope).
  • Ensuring horizontal coherence: digitalization affects competition, internal market, industry, employment, education, data protection, etc. The President's coordination functions allow her to:
    • Lead groups of commissioners or “clusters” to ensure digital policy coherence across portfolios.
    • Arbitrate conflicts between commissioners when a digital initiative affects several areas.
  • Politically representing the Commission in international forums on digital governance (G7, G20, UN, OECD, bilateral summits), defending the EU position developed by the Commission and supported by the Council.

4. Limits of her powers

No Treaty provision grants the President an exclusive or autonomous competence in digital matters separate from the College of Commissioners. All legislative and regulatory decisions are adopted collegially. The President's specificity is:

  • Her capacity to define priorities and organization.
  • Her central role in the political representation of the European digital agenda.
  • Her influence over the composition and coordination of the Commission.

In summary, according to the Treaties, Ursula von der Leyen does not have “digital powers” of her own but exercises, regarding digital transformation, the same functions of promotion, coordination, internal organization, and representation that the TFEU attributes to the Commission presidency in any other major Union priority.

What legal requirements must Member States meet to limit the presence of providers considered high-risk in their telecommunications networks according to current European legislation?

EU Member States can limit or exclude providers considered “high-risk” from their telecommunications networks (particularly 5G), but only if they comply with a series of legal requirements derived from Union Law and common political guidelines (the so-called EU 5G Toolbox). These are not discretionary decisions: they must be anchored in an appropriate legal basis and respect principles such as proportionality, non-discrimination, and the internal market.

1. Legal basis and Member State competence

First, the Member State must act within its competences in:

  • National security (essentially a state competence, but exercised respecting EU Law).
  • Cybersecurity and electronic communications, where the following apply:
    • The European Electronic Communications Code (Directive (EU) 2018/1972).
    • Cybersecurity legislation, including the NIS Directive and its revision NIS2.
    • The Commission Recommendation on 5G network cybersecurity and the “5G Toolbox.”

Restrictions must have a clear foundation in national legislation that transposes or develops these rules, defining who decides, by what procedure, and with what criteria.

2. Prior risk assessment based on objective criteria

It is not acceptable to declare “high risk” in a generic or purely political manner. Member States must:

  • Conduct a security risk assessment of their networks (especially 5G and critical elements).
  • Apply objective technical and legal criteria, including:
    • The provider's role in critical functions (network core, management, orchestration, data centers, etc.).
    • The degree of technological dependence and risk of “vendor lock-in.”
    • Security history, known vulnerabilities, and capacity for remediation.
    • Possible third-country state interference (e.g., legal frameworks obliging the provider to cooperate with intelligence services without sufficient safeguards).

The EU 5G Toolbox emphasizes that the concept of “high-risk provider” must derive from this structured assessment, not from a purely geopolitical or commercial criterion.

3. Proportionality and non-discrimination

Limiting high-risk providers involves interfering with freedom of enterprise and the free movement of goods and services. Therefore, EU law requires:

  • Measures proportionate to the detected risk:
    • Prioritize restrictions on critical components and functions (network core, remote management, monitoring systems).
    • Only reach a total exclusion of the provider if risks cannot be mitigated otherwise.
    • Allow, when reasonable, transitional periods and gradual replacement plans.
  • No arbitrary discrimination:
    • Measures must be based on concrete risks, not on national origin per se.
    • The same criteria must apply to all providers in comparable situations.

4. Respect for the internal market and European coordination

National decisions cannot ignore the functioning of the EU internal market:

  • Restrictions must be compatible with competition and public procurement rules.
  • If they constitute a new “technical regulation,” they must follow European prior notification procedures, so the Commission and other Member States can examine their impact.
  • States must coordinate through European structures (e.g., the NIS Cooperation Group and the 5G expert group) to avoid fragmentation and ensure an equivalent security level.

5. Procedural guarantees and judicial review

Measures against high-risk providers must respect the guarantees of the Rule of Law:

  • Reasonable transparency about the criteria used and the type of measures (without revealing sensitive security information).
  • Clear procedure for decision-making (competent body, deadlines, information to operators).
  • Right of defense for the provider and affected operators, at least through access to sufficient reasoning.
  • Possibility of appeal before national courts or independent regulatory bodies, with proportionality and EU law compatibility review.

6. Comprehensive risk management approach

Finally, European legislation and the 5G Toolbox adopt a global approach: limiting high-risk providers is only one piece of a broader cybersecurity strategy, which includes:

  • Enhanced security requirements for essential operators and important service providers.
  • Business continuity and incident response plans.
  • Continuous regulatory supervision and updating of risk assessments in light of new technological or geopolitical threats.

Overall, Member States can only restrict high-risk providers when doing so is legally founded, based on an objective risk assessment and coordinated at the European level, with proportionate, non-discriminatory measures subject to effective judicial review.

Could you specify exactly what role the European 5G Toolbox plays in identifying high-risk providers? What examples are there of Member States that have already applied restrictions to high-risk providers in 5G and how have they legally justified them? How is coordination between national cybersecurity legislation and obligations derived from the NIS2 Directive for 5G networks practically articulated?

Play

Test your knowledge with FREN!

How much do you know about this topic? Answer the following 3 questions.

What is one of the main objectives of the European Union's new digital regulatory offensive?

Question 1 of 3

Which system has been banned in the European Artificial Intelligence regulation to protect against the generation of non-consensual sexual content?

Question 2 of 3

What measure has the European Commission proposed to simplify cybersecurity incident management?

Question 3 of 3